

Events
Jenny Speck to Speak at Lockton U.S. Energy Risk Summit
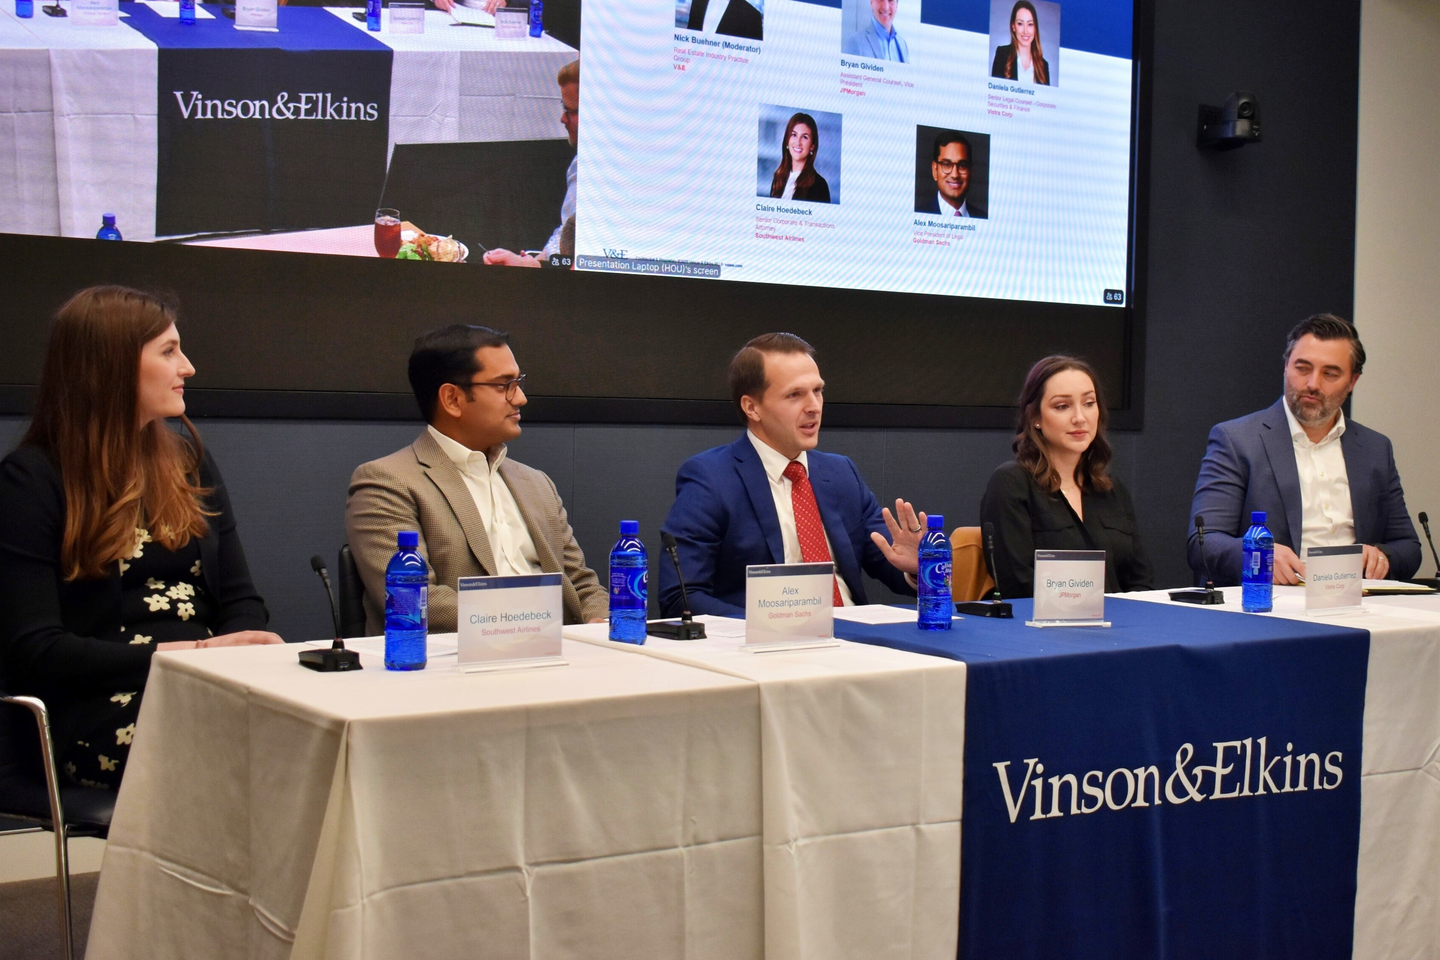
Partner Jenny Speck will speak at Lockton’s U.S. Energy Risk Summit on November 12, 2026, in Houston, Texas. The summit …
November 12, 2026
November 12, 2026 • 1-minute read


Insight
Client Alerts
V&E Cybersecurity Update
March 13, 2023 • 3-minute read
After a rash of significant cybersecurity breaches and ransomware attacks affecting companies across industries, the Biden administration released its much-anticipated National Cybersecurity Strategy on March 2, 2023. The plan builds upon the Biden administration’s previous efforts to protect the country’s cyberspace from malicious actors and hints at new cybersecurity regulations for critical infrastructure.
Biden’s National Cybersecurity Strategy structures itself around five pillars, emphasizing particular areas in which the administration seeks to “build and enhance” collaboration between the public and private sectors to strengthen cybersecurity.1 The five pillars are:
As part of its plan, the administration intends to use existing federal authorities to place new cybersecurity regulations on critical infrastructure, including oil and gas assets and pipelines. These anticipated regulations will “define minimum expected cybersecurity practices” in their industry, and notably will leverage existing cybersecurity frameworks, such as the Cybersecurity and Infrastructure Agency (CISA)’s Cybersecurity Performance Goals2 and the National Institute of Standards and Technology (NIST)’s Framework for Improving Critical Infrastructure Cybersecurity (NIST CSF).3 NIST CSF is currently being updated, with an initial draft of version 2.0 of the standard set to be published later this month. Owners of critical infrastructure should consider following the updates to the NIST CSF, as they could influence future regulations.
At the center of this effort to improve critical infrastructure cybersecurity are Sector Risk Management Agencies (SRMAs)4—federal agencies tasked with improving security within their sectors. The federal government plans to invest in SRMAs, with the goal that they will “proactively respond to the needs of critical infrastructure owners and operators” in their service areas. Hand in hand with this new investment, SRMAs will likely be used to develop and implement new cybersecurity regulations. In fact, some have already done so. For example, the Transportation Security Agency (TSA) has issued directives regulating the cybersecurity of pipelines and railroads. Other SRMAs, such as the Department of Energy and the Environmental Protection Agency, which have jurisdiction over the Energy Sector and the Water and Wastewater Systems Sector respectively could issue cybersecurity regulations in the future. Any of the sixteen distinct critical infrastructure sectors could face new cybersecurity regulations.
Beyond adding industry-specific regulations, the administration also intends to more broadly realign incentives in the cybersecurity space. The administration envisions two ways of achieving better incentives.
First, the administration plans to collaborate with Congress and the private sector on legislation placing liability for insecure software on manufacturers and software publishers. Paired with this increased liability, this hypothetical legislation would provide a safe harbor based on existing standards (like the NIST Secure Software Development Framework)5 to shield complying software companies from liability for vulnerabilities.
Second, the administration aims to scale public-private collaboration on cybersecurity through enhanced cooperation between CISA and SRMAs and sector-specific information sharing groups for the private sector as well as through increased federal grants and research and development on cybersecurity.
The Biden administration’s National Cybersecurity Strategy demonstrates the federal government’s appreciation of the serious threat that cyber attacks pose to the country’s most vital industries. Critical infrastructure owners can expect future government regulations that set minimum standards for cybersecurity and are based on existing cybersecurity frameworks. Companies should consider whether proactive adoption of an existing cyber framework or standard is appropriate for their business.
V&E assists clients in identifying, managing, and mitigating data privacy and cybersecurity risks, from early planning and assessment to managing incident response and resulting litigation.
1 National Cybersecurity Strategy (Mar. 2023), https://www.whitehouse.gov/wp-content/uploads/2023/03/National-Cybersecurity-Strategy-2023.pdf.
2 Comput. Info. Sec. Agency, Cross-Sector Cybersecurity Performance Goals (2022), https://www.cisa.gov/sites/default/files/2023-01/2022_00092_cisa_cpg_report_508c.pdf.
3 Nat’l Inst. Standards & Tech., Framework for Improving Critical Infrastructure Cybersecurity Version 1.1 (2018), https://nvlpubs.nist.gov/nistpubs/CSWP/NIST.CSWP.04162018.pdf.
4 Sector Risk Management Agencies, Comput. Info. Sec. Agency, https://www.cisa.gov/topics/critical-infrastructure-security-and-resilience/critical-infrastructure-sectors/sector-risk-management-agencies.
5 Nat’l Inst. Standards & Tech., Secure Software Development Framework (SSDF) Version 1.1 (2018), https://nvlpubs.nist.gov/nistpubs/SpecialPublications/NIST.SP.800-218.pdf.
This information is provided by Vinson & Elkins LLP for educational and informational purposes only and is not intended, nor should it be construed, as legal advice.
Discover our latest:
Events
Jenny Speck to Speak at Lockton U.S. Energy Risk Summit
Partner Jenny Speck will speak at Lockton’s U.S. Energy Risk Summit on November 12, 2026, in Houston, Texas. The summit …
November 12, 2026
November 12, 2026 • 1-minute read
CLE Events
Sixth Annual Navigating the Annual Meeting and Reporting Season
Join leading practitioners and industry voices for a timely discussion of the legal, regulatory, and governance developments shaping the next proxy season.
November 11, 2026
November 11, 2026 • 2-minute read

Client Alerts
Fifth Circuit Rejects CFIUS Preemption Challenge to Texas’s Lone Star Infrastructure Protection Act
On October 16, 2026, the United States Court of Appeals for the Fifth Circuit issued its decision in GH America …
November 3, 2026
November 3, 2026 • 9-minute read

Events
Jenny Speck Speaking at 2026 AFCC Global Biobased Economy Conference
Partner Jenny Speck will speak at the 2026 AFCC Global Biobased Economy Conference & Exhibit in a session titled “Tax …
November 3, 2026
November 3, 2026 • 1-minute read

Articles
Executive Order 14421: Managing the Risk of a Ban on Chinese Grid Equipment
The nation’s electric grid depends heavily on foreign-made equipment, much of it from China. Depending on how the Dept. of …
October 30, 2026
October 30, 2026 • 1-minute read

Deals & Cases
Vinson and Elkins advised Atlas Energy Solutions ProjectCo, LLC in a $424 million committed senior secured bridge facility with Goldman …
November 3, 2026
November 3, 2026 • 1-minute read

Deals & Cases
Vinson & Elkins advised CVR Energy, Inc. (NYSE: CVI) on its definitive agreement with subsidiaries of Marathon Petroleum Corporation (NYSE: …
November 3, 2026
November 3, 2026 • 1-minute read

Awards & Rankings
The Legal 500 Latin America guide recognizes Vinson & Elkins in the International Arbitration and Projects and Infrastructure categories. The …
November 2, 2026
November 2, 2026 • 1-minute read

Media Coverage
Stephanie Noble Featured in Energy & Mineral Law Foundation Member Spotlight
Partner Stephanie Noble was featured in the Energy & Mineral Law Foundation (EMLF) Member Spotlight, where she discussed her path …
October 28, 2026
October 28, 2026 • 1-minute read

Deals & Cases
Vinson & Elkins advised GridStor in connection with the financing of White Tank, a 100 MW / 400 MWh stand-alone …
October 28, 2026
October 28, 2026 • 1-minute read

Articles
Innovation and Investment: The Next Frontier in Aerospace and Defense
Vinson & Elkins Partners Sebastian Tiller and Ben Heriaud sit down for a conversation on the firm’s Aerospace and Defense …
November 3, 2026
November 3, 2026 • 6-minute read

Articles
Law Is a Practice. So Is Business Development.
Randi Revisore, Lauren Alford, and DeAnna Englezos reflect on two years of success leading BD Lab — Vinson & Elkins’ …
July 14, 2026 • V&E+ | Values
July 14, 2026 • 7-minute read
Articles
Data Center Dealmakers: A New Era of Power and Compute
Vinson & Elkins Partners Creighton Smith and Milam Newby share the story behind a groundbreaking AI infrastructure transaction — and …
June 15, 2026 • V&E+ Ventures
June 15, 2026 • 5-minute read

Client Alerts
Mid-Level Mindset: Empowering Lawyers Through a Pivotal Career Stage
Vinson & Elkins’ inaugural Mid-Level Associate Summit brought lawyers from across the firm to Houston for three days of learning …
March 31, 2026
March 31, 2026 • 5-minute read

Client Alerts
Pro Bono at Vinson & Elkins: Lawyers Changing Lives
Pro Bono Counsel Parker Cragg reflects on a life dedicated to service, returning to Vinson & Elkins, and wisdom he has picked up along the way.
October 20, 2025 • V&E+ Values
October 20, 2025 • 6-minute read

Thoughts or questions? Send us a note, and we’ll connect you with the right person.

our People
Please note that any communication with Vinson & Elkins via e-mail through this website does not constitute or create an attorney-client relationship with V&E. Please do not send any confidential information. A conflicts-of-interest procedure must be completed by V&E prior to establishment of an attorney-client relationship. When you execute an engagement letter from V&E you will be our client, and you may then exchange information freely with a V&E attorney.
By clicking “Accept,” you agree that we may review any information you transmit to us. You recognize that our review of your information, even if it is highly confidential and even if it is transmitted in a good faith effort to retain us, does not preclude us from representing another client directly adverse to you, even in a matter where that information could and will be used against you.